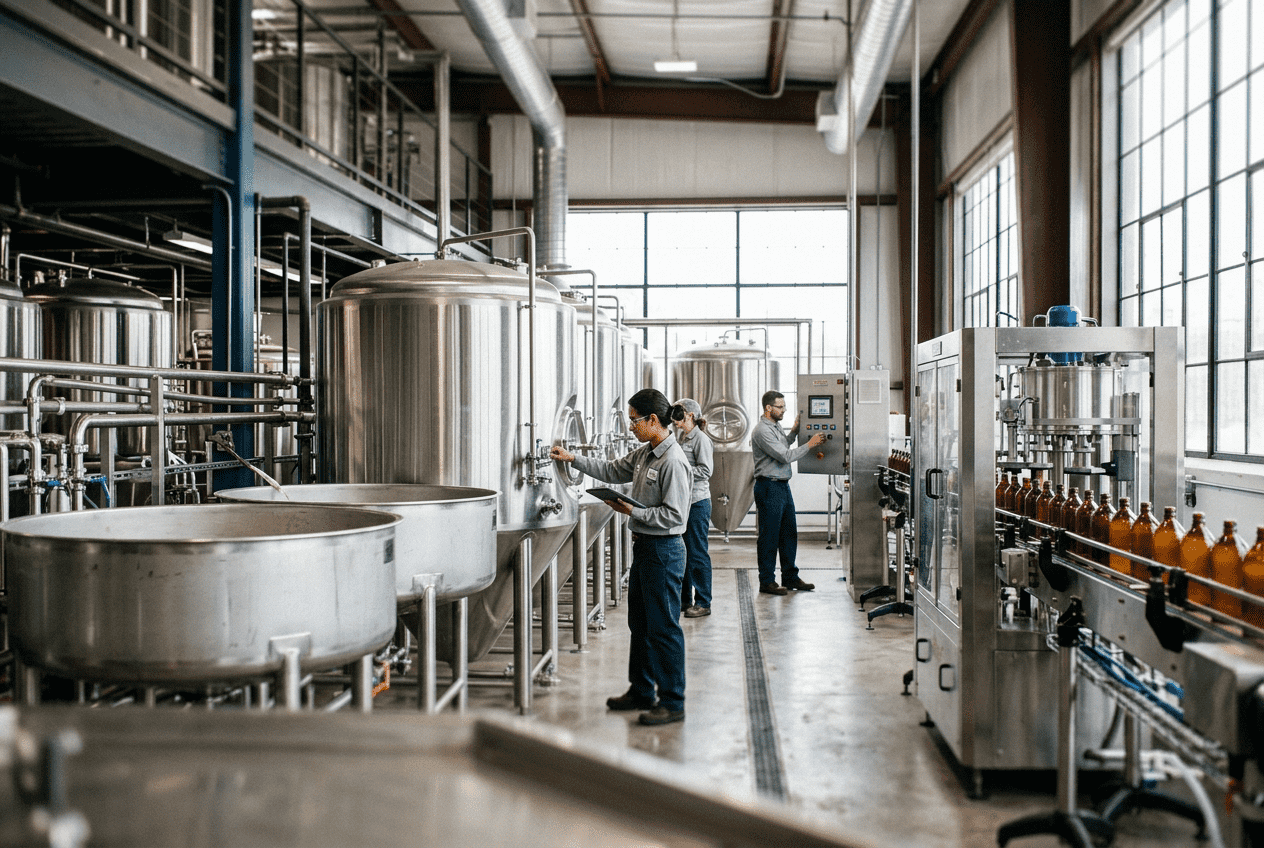
2026 Food Plant Emergency Shutdown System Design Guide for Process Safety
[trp_language language=”en_US”]
Emergency Shutdown System Design for Food Processing Facilities in the United States
Emergency shutdown system design in a U.S. food plant is not just an electrical or controls task. It is a process safety strategy that must isolate hazards, protect personnel, prevent ignition, preserve sanitation boundaries where practical, and allow a facility to return to production quickly after an event. In food and beverage operations, the best ESD program combines clearly defined shutdown zones, fail-safe field devices, code-compliant power isolation, coordinated PLC and SCADA logic, documented testing routines, and a hazard analysis that matches the real process risks on site. For operators in major production regions such as Chicago, Dallas-Fort Worth, Fresno, Atlanta, Charlotte, Houston, Kansas City, Omaha, and the Inland Empire, that means designing systems that work equally well in greenfield plants, brownfield retrofits, cold storage expansions, aseptic rooms, bottling halls, and protein processing lines.
The U.S. market is moving toward more integrated shutdown strategies because modern plants are more automated, more utility-dense, and more dependent on continuous throughput. A simple hardwired e-stop loop is rarely enough in a facility with ammonia refrigeration interfaces, clean-in-place skids, batching systems, retort lines, high-speed fillers, boiler rooms, compressed air, process wastewater handling, and high horsepower packaging assets. At the same time, over-design can create nuisance trips, sanitation delays, and excessive restart costs. The practical goal is selective, safe, code-aligned shutdown.
For project owners evaluating a new system, the smartest buying advice is to start with hazard ranking and operational zoning before hardware selection. Many plants first ask which safety relay, PLC, or disconnect to buy, but the higher-value question is which scenarios must stop instantly, which assets must coast to a controlled stop, which utilities must remain live for life safety, and which operations need product containment to avoid contamination or spoilage. That is especially important in sectors such as dairy, prepared foods, brewing, beverage co-packing, aseptic processing, seafood, and ready-to-eat proteins, where process continuity and safety have to be balanced carefully.
Across the United States, implementation trends for 2026 include deeper use of safety-rated PLCs, segmented network architectures, diagnostics-rich field devices, digital test logging, cybersecurity controls for shutdown logic, and sustainability-driven shutdown sequences that reduce water loss, product waste, and uncontrolled dumping. Policy pressure is also rising through insurer scrutiny, owner standards, and closer alignment between process safety expectations and electrical compliance practices. Food manufacturers near ports and trade corridors such as Los Angeles/Long Beach, Savannah, Newark, Tacoma, and Houston are also investing more in resilient shutdown design as supply-chain volatility makes unplanned downtime more expensive.
Quick Answer

An effective emergency shutdown system for a food plant in the United States should be based on six core decisions: define credible hazards, divide the plant into shutdown zones, assign fail-safe actions by equipment type, comply with NFPA 70 NEC and related electrical requirements, integrate shutdown logic with process automation without weakening independence, and maintain the system through scheduled testing and documentation. In practice, that means a refrigerated protein plant in Omaha will need different shutdown priorities than a beverage blending and packaging site in North Carolina or an aseptic dairy facility in California.
Most food and beverage facilities benefit from a layered ESD approach:
- Manual emergency stop stations for operators and maintenance staff
- Automatic trip inputs from pressure, temperature, gas detection, motor protection, fire alarm, or utility faults
- Safety logic solvers or safety PLCs with validated I/O behavior
- Final elements such as shunt trips, motor contactors, safety-rated valves, damper controls, and utility isolation devices
- SCADA visibility for alarm status, event history, permissives, and restart management
From a market perspective, U.S. food manufacturers are spending more on shutdown modernization in brownfield facilities than on purely new greenfield systems, because legacy plants often have mixed-voltage assets, undocumented wiring, older PLC generations, and disconnected maintenance records. Product types commonly included in an ESD scope are line e-stops, utility shutdown panels, gas valve trains, pump interlocks, conveyor isolation, boiler room interfaces, refrigeration tie-ins, retort safeties, mixer and grinder stops, and area annunciation. Buyers should prioritize system simplicity, device availability, environmental ratings, sanitation compatibility, and ease of annual proof testing.
| Plant Area | Typical Hazard | Recommended ESD Action | Control Priority | Restart Complexity | Notes |
|---|---|---|---|---|---|
| Raw receiving | Conveyor entanglement, vehicle interface | Stop localized conveyors and dock equipment | Medium | Low | Keep adjacent utilities active unless hazard spreads |
| Mixing and batching | Overpressure, chemical addition error | Close feed valves, stop agitators, isolate pumps | High | Medium | Sequence should preserve vessel integrity |
| Thermal processing | Steam, pressure, burn risk | Controlled stop with venting and lockout logic | High | High | Retort and UHT systems need defined depressurization rules |
| Packaging hall | Mechanical pinch points, accumulation jams | Stop affected line zones with upstream/downstream logic | Medium | Medium | Avoid plant-wide nuisance trips |
| CIP system | Chemical exposure, pump deadhead | Shut pumps, isolate chemical feeds, annunciate | High | Medium | Need flush and recovery procedure |
| Utility room | Electrical fault, gas leak | Isolate source, trip equipment, keep life-safety loads | Critical | High | Must align with NEC and utility coordination studies |
The table above shows why a single shutdown philosophy rarely fits every process area. Good design aligns the action to the hazard, not just to the equipment list.
The market growth trend reflects a practical reality: as automation intensity rises and downtime costs climb, plants increasingly treat emergency shutdown architecture as a capital risk-management tool rather than a narrow compliance purchase.
ESD System Architecture and Component Selection

System architecture should start with a documented cause-and-effect matrix. That matrix connects initiating events to logic actions and final elements. For example, a high-high pressure event in a syrup blending skid may need to stop positive displacement pumps, close inlet valves, hold vessel venting logic, generate a horn/beacon alert, and block restart until operator verification is complete. A line e-stop in a packaging lane may only need to de-energize motion equipment in that lane while preserving refrigeration, compressed air, and adjacent fillers.
In U.S. food facilities, the most common architecture types are hardwired relay systems, hybrid relay-plus-PLC systems, and safety PLC platforms. Hardwired systems are simple and transparent, but they can become difficult to scale in plants with many zones. Hybrid systems are common in mid-size facilities where certain safety functions remain independent while automation supervises status and recovery. Safety PLC systems support more diagnostics, sequence control, and selective shutdowns, but they demand stronger specification, validation, and cybersecurity discipline.
Component selection should account for washdown exposure, corrosive chemicals, temperature extremes, and maintenance access. In a poultry plant in Arkansas or a seafood site in the Pacific Northwest, NEMA enclosure ratings and hygienic mounting details can be as important as the electrical rating itself. In beverage plants with frequent caustic and acid cleaning, pushbuttons, pull cords, and junction boxes should be chosen for chemical resistance and easy replacement.
| Component | Primary Function | Selection Criteria | Common Food Plant Use | Preferred Failure Mode | Buyer Tip |
|---|---|---|---|---|---|
| Emergency stop pushbutton | Manual shutdown initiation | NEMA rating, visibility, glove use | Packaging lines, mixers, conveyors | Fail to safe | Standardize colors and device families plant-wide |
| Safety PLC | Logic solving and diagnostics | SIL/PL suitability, expansion, support | Multi-zone plants, utility integration | Safe-state on fault | Verify local programming support availability |
| Safety relay | Dedicated safety logic | Circuit simplicity, reset behavior | Single machine cells | De-energize output | Use where flexibility is not needed |
| Shunt trip breaker | Electrical isolation | Coordination, breaker compatibility | Utility and MCC shutdowns | Trip open | Review with short-circuit study |
| Solenoid isolation valve | Flow shutoff | Media compatibility, fail position | Steam, gas, water, product transfer | Normally closed where appropriate | Match valve action to process consequences |
| Horn and beacon | Alarm annunciation | Audibility, visibility, sanitation | High-noise rooms, utility areas | Alarm on trip | Use differentiated patterns by zone |
The component table matters because ESD performance depends on the last device in the chain as much as the controller. Plants often invest in advanced controls while leaving weak final elements in place. That creates a false sense of safety.
From a technology capability standpoint, Disruptive Process Solutions supports integrated process, electrical, and controls engineering for food and beverage clients across North America. That multidisciplinary capability is important for ESD work because shutdown design touches PLC programming, SCADA visibility, utility coordination, equipment interfaces, and mechanical process behavior at the same time. A line can only shut down correctly if controls logic and process design were developed together.
NFPA 70 NEC Compliance for Emergency Shutdown

NEC compliance is fundamental because emergency shutdown systems operate inside the broader electrical infrastructure of the facility. While ESD design also intersects with machinery safety, fire protection, and insurer requirements, NFPA 70 sets the baseline for wiring methods, disconnecting means, overcurrent protection, equipment installation, hazardous area considerations where applicable, grounding, working clearances, labeling, and maintenance implications. In food plants, compliance mistakes often appear during expansions when new process skids are connected to existing MCCs, panelboards, utility feeds, or control networks without a coordinated review.
Emergency shutdowns should not create unintended electrical hazards. For instance, tripping a feeder without considering downstream control power, loss of ventilation, or recovery state can make an event worse. Likewise, disconnecting sanitation systems or freezer door controls in the wrong sequence can introduce secondary operational risks. NEC-aligned design therefore needs one-line review, arc flash implications, selective coordination strategy where needed, enclosure suitability, and field labeling consistency.
Facilities in industrial corridors like Houston, New Jersey, Memphis, and Southern California often operate under aggressive production schedules, so brownfield shutdown upgrades must be designed for phased installation. That makes lockable disconnect locations, temporary feeds, panel separation, and commissioning windows especially important.
| Compliance Topic | NEC Design Concern | Why It Matters to ESD | Typical Plant Issue | Recommended Action | Verification Method |
|---|---|---|---|---|---|
| Disconnecting means | Accessible isolation points | Allows safe emergency de-energization | Buried or remote disconnects | Relocate or add local means | Field walkdown |
| Wiring methods | Wet and washdown suitability | Prevents failure during emergency use | Corroded fittings, moisture ingress | Upgrade conduit, seals, glands | Installation inspection |
| Overcurrent protection | Breaker/fuse selection | Supports reliable trip performance | Mismatched protective devices | Review coordination study | Power study update |
| Grounding and bonding | Fault clearing effectiveness | Reduces shock and equipment damage risk | Improper bonded skid additions | Inspect and correct grounding paths | Continuity testing |
| Equipment labeling | Identification and hazard communication | Improves emergency response speed | Inconsistent panel naming | Standardize labels and directories | Documentation audit |
| Working clearance | Service access safety | Ensures maintainable shutdown hardware | Panels blocked by process additions | Reconfigure layout or relocate assets | Code clearance check |
The compliance checklist above is useful because many ESD failures are not logic failures; they are installation failures. A perfect sequence in software cannot overcome inaccessible disconnects, degraded enclosures, or poor field labeling.
For buyers, the practical advice is to request a shutdown scope that includes electrical field verification, panel schedules, one-line updates, and a commissioning checklist tied to code compliance. If that work is not included, owners often discover expensive rework late in the project.
Integration with Process Control and Automation
Integration is where shutdown systems become truly valuable. An isolated e-stop circuit can stop equipment, but an integrated ESD can also preserve data, guide operators, prevent conflicting commands, and support faster recovery. In food processing, integration usually involves PLCs, HMI screens, SCADA historians, VFD status, recipe systems, utility controls, and alarm management. The key rule is that visibility and coordination can be integrated, but the safety function itself should remain robust and fail-safe.
For example, when a filler room zone trips in a high-speed RTD beverage plant, the control system may need to stop depalletizers, cap feeders, labelers, and packers in staged logic while logging the event, preserving fault context, and preventing upstream overflow. In a protein grinding room, shutdown integration may need to stop grinders and augers immediately while allowing extraction or sanitation support systems to continue under controlled conditions. In an aseptic process, the sequence may include diversion, hold, sterile boundary protection, and quality event capture.
Industry demand for integrated ESD is strongest in sectors with dense automation and expensive restarts.
The bar chart shows why automation-linked shutdown design is especially relevant in beverage, aseptic, and protein operations where throughput, quality, and hazard exposure are closely coupled.
Technologically, DPS works in the space where process engineering and automation meet. Its teams handle controls engineering, PLC programming, SCADA integration, and broader system coordination as part of complete process projects. That capability is useful when shutdown actions must align with equipment behavior such as pasteurization, retort, distillation, fermentation, batching, water treatment, or CIP. Instead of treating ESD as an isolated cabinet package, an integrated team can connect the shutdown philosophy to the actual manufacturing process.
Local supplier strategy matters as well. U.S. plants often source safety hardware through regional electrical distributors near hubs like Charlotte, Milwaukee, Cincinnati, and Sacramento, while relying on national integrators for programming and startup. Owners should evaluate not only brand preference but also replacement lead times, field technician availability, and whether local maintenance teams already know the platform.
Zone-Based Shutdown Sequence Design
Zone-based design is the best way to prevent both underreaction and overreaction. Instead of tripping the entire plant for every event, a zone strategy defines which process areas, utilities, and material flows are linked to a given hazard. This approach is especially effective in large U.S. facilities with multiple packaging halls, utility yards, ingredient rooms, and segregated hygienic spaces.
A shutdown zone can be geographic, functional, or hazard-based. Geographic zones may separate raw processing from ready-to-eat packaging. Functional zones may isolate boiler house, refrigeration engine room, syrup room, or CIP center. Hazard-based zones may group all equipment affected by a flammable cleaning solvent interface, high-pressure steam network, or confined machinery line. The right structure depends on process flow, sanitation barriers, utility dependencies, and restart economics.
| Zone Type | Typical Equipment Included | Trigger Examples | Immediate Actions | Delayed Actions | Operational Goal |
|---|---|---|---|---|---|
| Packaging zone | Conveyors, fillers, labelers, packers | E-stop pull cord, guard open | Stop motion drives | Hold upstream feed after short delay | Protect operators and avoid pileups |
| Mixing zone | Tanks, pumps, dosing skids | High-high pressure, pump fault | Stop pumps, close inlets | Alarm batch hold | Protect vessel and product integrity |
| Thermal zone | Retort, UHT, heat exchangers | Temperature runaway, steam fault | Isolate energy source | Controlled depressurization | Prevent rupture and preserve safety |
| Utility zone | Boilers, compressors, RO, air systems | Electrical fault, gas alarm | Trip affected utility set | Notify dependent lines | Contain utility-side hazard |
| Chemical zone | CIP chemical tanks, dosing, pumps | Leak detection, transfer fault | Stop dosing, isolate valves | Drain or neutralize by procedure | Minimize exposure and contamination |
| Cold storage zone | Conveyors, doors, evaporator interfaces | Mechanical jam, local e-stop | Stop local movement | Maintain life-safety systems | Avoid unnecessary temperature loss |
The zone matrix above illustrates how selective shutdown protects both people and production. It is especially useful in facilities where one line issue should not dump the whole utility backbone.
Trend-wise, 2026 designs increasingly use digital zoning tied to visualization layers in SCADA. Operators can see which assets are in each shutdown boundary, which permissives are preventing restart, and which field devices must be reset. That reduces confusion during stressful events.
The area trend indicates a clear move toward smarter, narrower shutdown boundaries. That shift is driven by cost control, sustainability, and operator usability.
Testing and Maintenance Protocols for ESD
An ESD system that is not tested should be treated as an assumption, not a safeguard. Food manufacturers often install shutdown hardware during a project but fail to maintain proof-test discipline after startup. That is a serious weakness because washdown environments, vibration, sanitation chemicals, thermal cycling, and production changes can degrade system performance over time.
Testing should include field initiation devices, logic behavior, final element action, HMI and alarm indication, sequence timing, event logging, and restart permissives. Plants should define who owns each test: maintenance, controls, operations, EHS, or an outside specialist. The best protocol combines monthly visual checks, quarterly functional tests for selected devices, annual full-sequence validation, and change-management review whenever equipment is modified.
| Test Activity | Recommended Frequency | Responsible Role | What to Verify | Common Failure Found | Documentation Needed |
|---|---|---|---|---|---|
| Visual device inspection | Monthly | Maintenance | Damage, obstruction, corrosion | Broken pushbutton covers | Inspection log |
| E-stop functional test | Quarterly | Operations + Controls | Input recognition and equipment stop | Field wiring faults | Test record with timestamp |
| Valve stroke verification | Quarterly | Maintenance | Correct fail position and closure time | Sticky actuators | Stroke checklist |
| Alarm and SCADA audit | Semiannual | Controls engineer | Correct message, historian capture | Incorrect tag mapping | Alarm review report |
| Full cause-and-effect test | Annual | Cross-functional team | End-to-end sequence performance | Changed equipment behavior | Validation summary |
| Post-modification review | Every change | Project manager/EHS | Impact of new equipment or logic | Unreviewed bypasses | MOC package |
This maintenance schedule is effective because it separates routine inspection from full proof testing. Many facilities do one or the other, but reliable systems need both.
From a service capability perspective, companies that can design, install, integrate, and commission the system are often better positioned to create testable documentation. DPS uses a design-build-manage approach, meaning engineering intent, field execution, and startup coordination stay aligned through the project lifecycle. That matters when maintenance teams need accurate cause-and-effect lists, panel documentation, and realistic turnover packages rather than a stack of disconnected drawings. More detail on the firm’s project model is available on the company overview page.
Risk Assessment and Hazard Analysis Methods
Risk assessment should drive the shutdown philosophy, not merely validate it after the fact. In food and beverage facilities, hazard analysis must look beyond fire and shock to include pressure release, thermal injury, chemical exposure, rotating equipment, product contamination, sanitation interactions, utility dependency, and environmental release. A plant with ammonia refrigeration interfaces, high-pressure steam, or caustic CIP service needs a more rigorous methodology than a small dry-pack line with isolated conveyors.
Several methods are commonly used in the United States: process hazard analysis workshops, HAZOP-style reviews, what-if analysis, failure mode and effects analysis, machine risk assessment, and layer of protection thinking for higher-consequence systems. The best method depends on the process. A beverage blending line may benefit from what-if plus control narrative review, while a retort or aseptic project may need a more structured node-based analysis.
| Method | Best Use Case | Main Strength | Limitation | Typical Food Plant Application | Output for ESD Design |
|---|---|---|---|---|---|
| What-if analysis | Moderate complexity systems | Fast and practical | May miss deep interactions | Packaging and utility upgrades | Preliminary trip list |
| HAZOP-style review | Complex process nodes | Systematic deviation analysis | Time intensive | Aseptic, UHT, blending, CIP centers | Detailed cause-and-effect basis |
| FMEA | Equipment-focused studies | Good for component failure modes | Less process-oriented | Pumps, valves, skids, control panels | Final element reliability priorities |
| Machine risk assessment | Operator-machine interaction | Clear guarding and stop strategy | Limited utility scope | Conveyors, slicers, packaging assets | Local stop and access control logic |
| PHA workshop | Plant-wide hazard screening | Cross-functional perspective | Can stay high level | Brownfield expansions | Zone definitions and risk ranking |
| LOPA-style review | High-consequence scenarios | Clarifies safeguard sufficiency | Requires stronger data quality | Utility hazards, pressure events | Need for independent shutdown layers |
The reason this comparison matters is simple: if the analysis method is too shallow, the shutdown design will likely be too generic. Better hazard analysis usually leads to fewer unnecessary trips and stronger protection where it truly matters.
Applications vary by industry. Dairy plants often focus on CIP chemical handling, homogenization, and thermal loops. Protein facilities prioritize mechanical injury, sanitation chemical exposure, and refrigeration interfaces. Beverage sites emphasize high-speed packaging, CO2 systems, syrup handling, and utility resilience. Prepared foods operations may need integrated responses across cook, chill, fill, and freezer zones.
Design-Build Implementation Best Practices
Implementation success depends on more than design documents. In working U.S. food plants, shutdown projects must be installed around sanitation windows, production demands, utility outages, seasonal demand peaks, and inspection schedules. That is why design-build delivery can be effective for ESD modernization: engineering, procurement, field coordination, and commissioning are managed as one execution path rather than isolated tasks.
Best practices include early field walkdowns, existing condition verification, tagged photo surveys, sequence workshops with operators, spare parts standardization, phased panel cutovers, FAT/SAT planning, and restart training. Owners should require a shutdown narrative, I/O list, panel schedule updates, one-line revisions, cause-and-effect matrices, and operator reset procedures before construction starts. It is also wise to identify long-lead items and local substitute options in case preferred components are delayed.
Case studies in the U.S. market repeatedly show that the greatest savings come from solving the real bottleneck rather than buying the largest hardware package. On capital projects, that may mean revising PLC logic and zone boundaries instead of replacing every panel. On a relocation or expansion, it may mean integrating existing skids more intelligently instead of rebuilding proven equipment from scratch. Project examples and execution approaches can be explored through DPS project case studies.
On the manufacturing side, DPS not only integrates third-party systems but also supplies proprietary process equipment such as tanks, CIP systems, marination tumblers, and cooking vessels as part of broader plant solutions. That manufacturing capability can reduce interface risk on projects where shutdown logic must coordinate tightly with process skids, vessels, pumps, and utility tie-ins. The company’s available equipment solutions show how in-house and integrated assets can support a more cohesive plant design.
| Implementation Practice | Why It Works | Best Project Stage | Risk If Skipped | Owner Benefit | Typical Deliverable |
|---|---|---|---|---|---|
| Field verification before design freeze | Confirms actual wiring and assets | Concept and FEED | Late change orders | Budget accuracy | Existing conditions report |
| Zone workshop with operations | Captures real process behavior | Basis of design | Overly broad shutdowns | Higher uptime | Zone matrix |
| Phased cutover planning | Reduces outage duration | Construction planning | Extended downtime | Production protection | Cutover schedule |
| Device standardization | Simplifies maintenance and spares | Procurement | Mixed inventory burden | Lower lifecycle cost | Approved vendor list |
| Integrated FAT/SAT | Validates logic before startup | Commissioning | Field debugging under pressure | Safer startup | Test scripts and signoffs |
| Operator reset training | Prevents unsafe restart attempts | Turnover | Confusion after trip event | Faster recovery | SOP and training record |
The implementation table highlights a major truth of ESD projects: most expensive failures happen at interfaces, not inside the specification. Good design-build delivery reduces those interface gaps.
The comparison chart shows why many owners use both local suppliers and specialized integrators. Local distributors win on parts access, while integrated design-build partners usually outperform on process understanding, system coordination, and lifecycle support.
Our Company
Disruptive Process Solutions serves food and beverage manufacturers throughout all 50 U.S. states and Canada with a model built around engineering, construction coordination, and execution management. For clients planning emergency shutdown work, that matters because ESD is rarely a stand-alone purchase. It usually touches process equipment, utilities, controls, electrical distribution, startup sequencing, sanitation, and long-term operational strategy.
In technology, DPS brings process, mechanical, electrical, and controls expertise together, including PLC programming, automation, SCADA, utility integration, and system commissioning. In manufacturing, the company supplies selected proprietary process equipment that can be integrated into broader plant projects, helping reduce mismatch between equipment behavior and control intent. In service delivery, DPS operates through a design-build-manage structure that supports feasibility studies, capital planning, owner’s representation, engineering design, general contracting functions where applicable, installation oversight, and turnkey execution.
That model is especially useful for U.S. food and beverage plants that need practical shutdown strategies rather than generic templates. Whether the project involves a brewing operation in Colorado, a co-packer near Atlanta, a dairy expansion in Wisconsin, a prepared foods line in Texas, or an aseptic system in California, the objective is the same: build a shutdown plan that protects people and assets while supporting long-term profitability and maintainability.
FAQ
What is the difference between an e-stop system and a full ESD system?
An e-stop system usually focuses on immediate machine stopping at local operator access points. A full ESD system includes broader cause-and-effect logic, utility interfaces, zone actions, annunciation, and structured restart controls across process areas.
Do all food plants need a safety PLC?
No. Smaller or simpler systems may be better served by hardwired safety relays. Plants with multiple zones, utility interactions, advanced automation, or complicated restart states often benefit from safety PLC architecture.
How often should food plant emergency shutdown systems be tested?
Visual inspections should typically occur monthly, selected functional tests quarterly, and full sequence verification at least annually. Frequency may need to increase in harsh washdown or high-change environments.
Can an emergency shutdown damage product or sanitation conditions?
Yes, if the sequence is poorly designed. That is why zone-based and process-aware logic is important. The safest sequence should also consider product containment, pressure relief, and chemical isolation.
How does NEC compliance affect shutdown design?
It affects disconnecting means, wiring methods, enclosure suitability, overcurrent protection, grounding, labeling, and maintainability. ESD logic must be supported by code-compliant electrical infrastructure.
What industries benefit most from upgraded shutdown systems?
High-automation beverage plants, dairy processors, protein facilities, aseptic operations, prepared foods manufacturers, and utility-dense co-packing sites often see the biggest gains from modernized ESD design.
What should owners ask a supplier before buying?
Ask for shutdown narratives, cause-and-effect matrices, proof-testing strategy, spare parts plan, field verification scope, local support coverage, and brownfield cutover methodology. Also ask who owns startup and post-start optimization.
How do future trends affect 2026 projects?
Expect more diagnostics, cybersecurity review, segmented shutdown zones, digital test records, stronger insurer scrutiny, and sustainability-oriented sequencing that reduces water, product, and energy waste during trips.
In summary, a strong U.S. food plant emergency shutdown program is selective, documented, code-compliant, automation-aware, and maintained for the long term. Plants that treat ESD as part of overall process design, rather than as a late electrical add-on, usually achieve safer operations, fewer nuisance trips, and more reliable production performance.
[/trp_language]
Complete Company Portfolio

About the Author: Disruptive Process Solutions (DPS)
The DPS team combines process engineering expertise with real-world food and beverage manufacturing experience. Our content focuses on process optimization, production efficiency, facility improvements, and practical solutions that help manufacturers operate more effectively in a rapidly evolving industry.
Share

